Less operational effort
Inventory, prioritization and investigation in one place: fewer hours cross-referencing spreadsheets and logs.
a 33TS product — built by incident responders
EDR · VULNERABILITY MANAGEMENT · ZTNA
See where vulnerabilities are, investigate threats and control who accesses your systems. EDR, vulnerability management and zero trust in one agent.
AI investigates. You choose: human approval or autopilot.
FOR IT AND SECURITY TEAMS · FROM 25 ENDPOINTS
EXPOSURE
THREATS
ACCESS
01 / VISIBILITY
Prioritize the flaws that matter.
02 / RESPONSE
Evidence before action.
03 / ACCESS
Only the authorized resource.
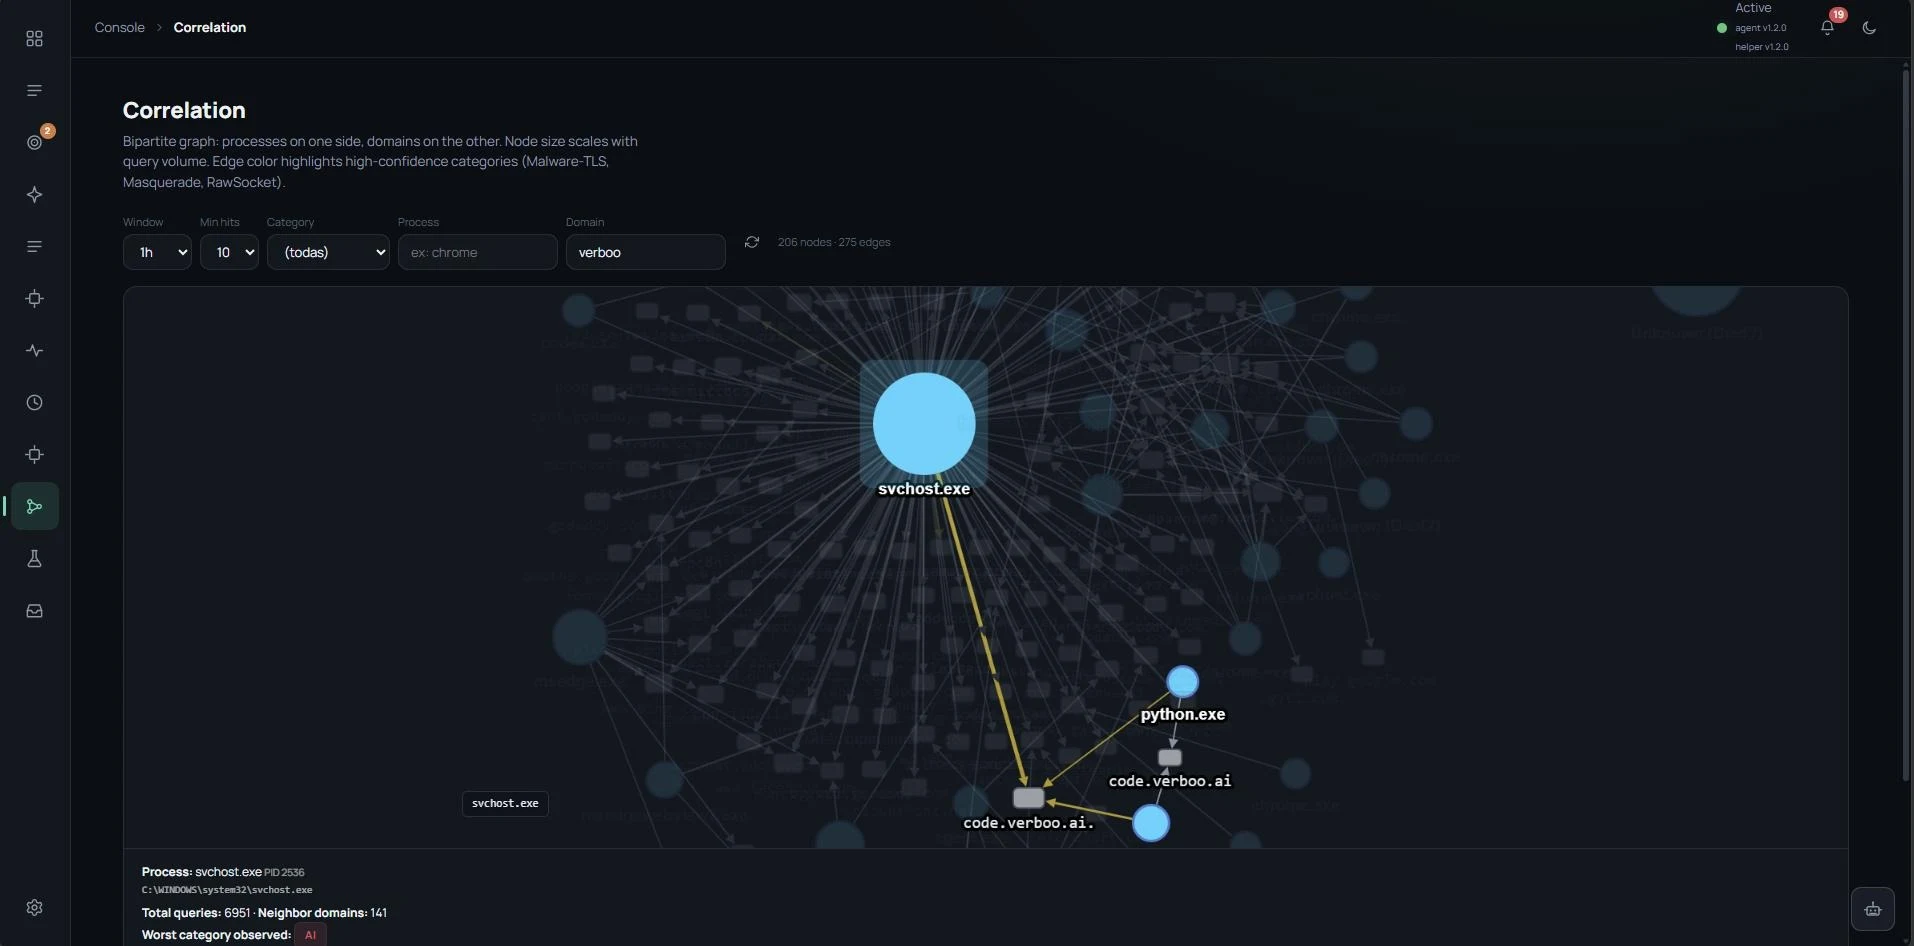
A flaw in the scanner. An alert in EDR. A connection through the VPN. When signals are separate, your team has to reconstruct the story. dome brings that context together to support decisions.
EDR
Vulnerability scanner
Patch / RMM
VPN / ZTNA
Inventory
Compliance spreadsheet
BUSINESS OUTCOMES
At the end of the day, a company does not want to buy an EDR or a ZTNA. It wants to reduce risk, keep the operation running and justify the investment. dome connects the technology to that outcome.
Inventory, prioritization and investigation in one place: fewer hours cross-referencing spreadsheets and logs.
AI correlates signals and presents evidence; decisions take minutes, not days.
One agent and one console instead of several tools, with a clear per-endpoint cost.
Gaps, evidence and audit reports ready to show results to the board.
01 / THE PLATFORM
EDR, vulnerability management and zero trust connected in one agent. Less context lost between tools.
Exposure & Vulnerability Management
See which machines have flaws and what to fix first. EOL means end of vendor support; a patch is an update that closes the flaw.
EDR + AI investigation
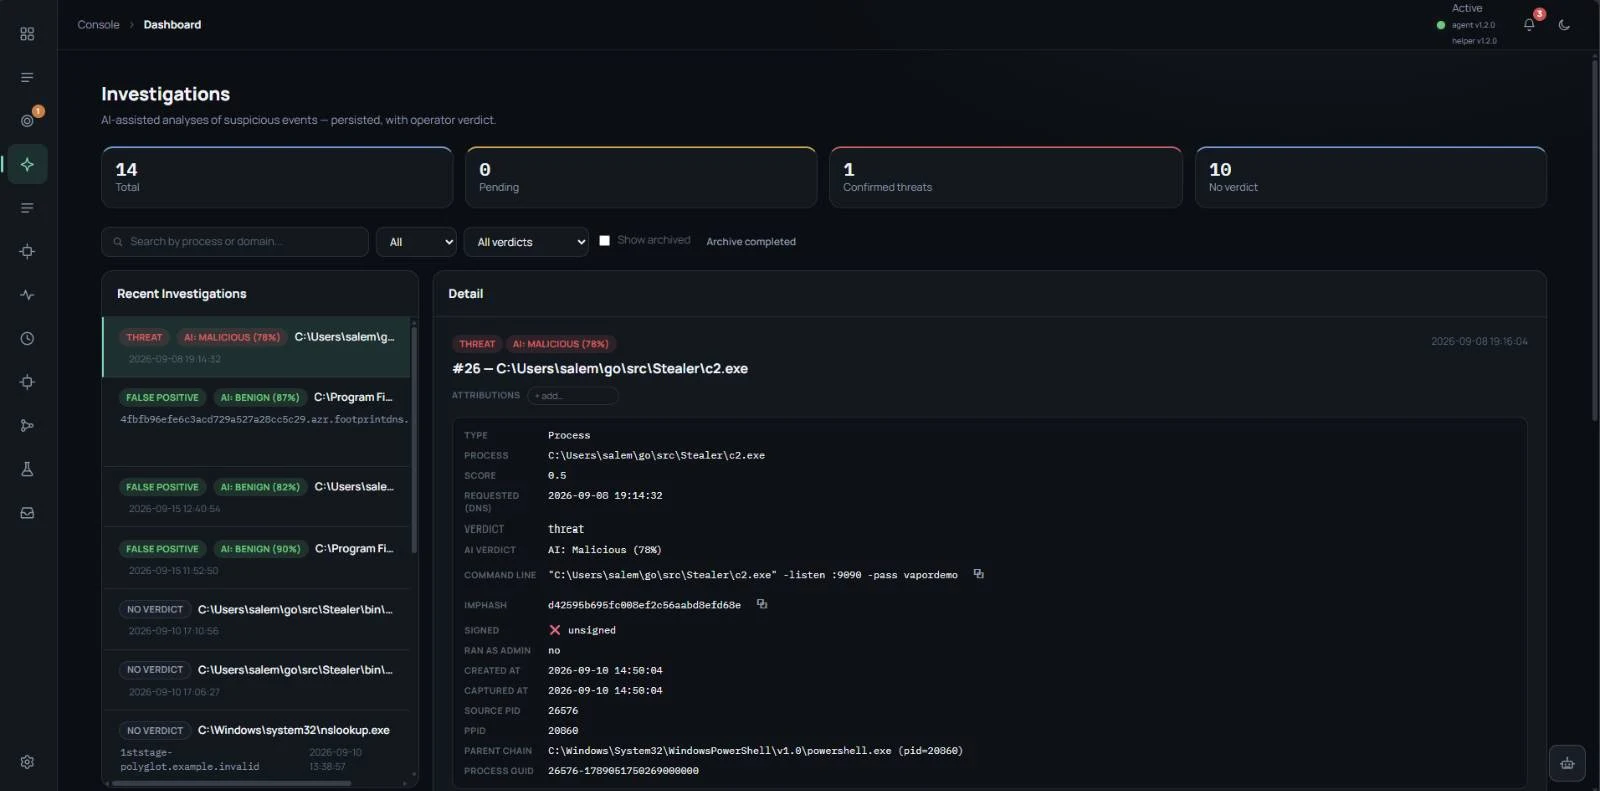
Spot signs of intrusion, gather evidence and recommend a response. You choose whether each action waits for approval or runs immediately.
Native ZTNA
Grant only the approved system to a verified person on a secure machine. If the machine becomes unsafe, access is blocked.
Audit evidence, immutable trail and financial risk with FAIR / ROSI. The technical view, translated for decisions.
From a flaw to restored access, with context and the level of autonomy you set.
Vulnerability found
Attack attempts exploitation
dome detects; AI explains
You approve (or autopilot)
Machine isolated; ZTNA revoked
Patch applied
Access restored
Audit report
03 / ONE AGENT VS. SEPARATE TOOLS
Protection, vulnerabilities, patching and access are usually bought separately. See the difference in your team’s routine.
dome · One agent for protection, vulnerabilities, patching and access.
Separate · One agent per tool, each with its own install, updates and conflicts.
Gain · Simpler rollout and less load on devices.
dome · One screen with inventory, alerts, flaws and access.
Separate · One console per vendor; the team cross-references data by hand.
Gain · Less time switching screens and rebuilding context.
dome · Detection, AI investigation and remediation in one flow.
Separate · The alert starts in one tool, the patch in another, access in a third.
Gain · Faster response, without handing the case between systems.
dome · Human approval or autopilot, configured by the customer.
Separate · Different automation rules in each tool.
Gain · One policy, with every decision logged.
dome · One contract, priced per endpoint.
Separate · Several contracts, renewals and billing models.
Gain · Predictable spend that is easier to justify.
dome · Evidence of protection, fixes and access in one place.
Separate · Reports exported from each system and merged by hand.
Gain · Accountability ready for leadership and auditors.
A comparison of functions, not performance. Gains depend on your environment and plan; zero-trust access is in the Complete plan.
AI GOVERNANCE
In a corporate environment, a misfired automation can be as serious as an incident. That is why dome makes explicit who decides what — and logs every step.
It investigates, correlates signals, prioritizes vulnerabilities and recommends responses — always with evidence.
Each response action waits for your approval — or runs on autopilot, if you configure it that way. By policy, by severity, by environment.
Every decision, human or automatic, is logged with the evidence behind it — ready for auditing.
Isolating a machine is not a one-way street: once the issue is fixed, access is restored and the history is preserved.
INTEGRATIONS
A company that has already invested in technology will not replace everything at once. dome is designed to work alongside your environment — and native integrations are expanding. Bring us your scenario.
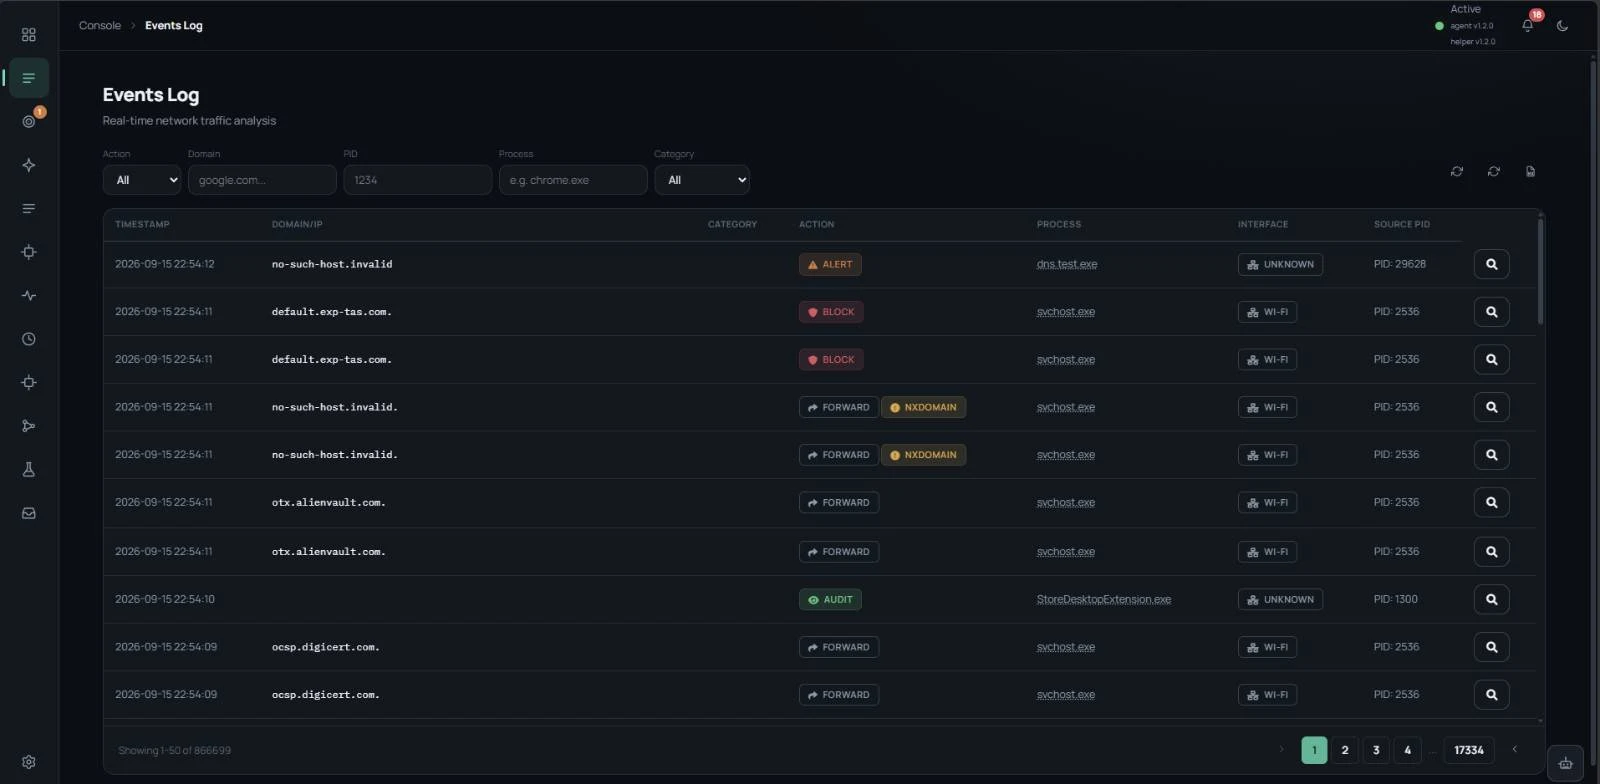
dome events and verdicts sent to your SIEM for central correlation.
Tickets opened with context: evidence, affected machine and recommended action.
Identity as the basis for access: groups and accounts from the directory you already use.
Endpoints, servers and cloud under the same inventory and the same policies.
AI investigates. You approve — or switch on autopilot. The agent executes.
Agent detects suspicious behavior.
AI correlates signals: C2 communicates with the attacker; DGA generates domains to conceal that communication.
You review the evidence and approve — or, on autopilot, dome acts right away.
Process stopped, file quarantined or machine isolated.
Identity verified with a certificate and MFA — more than one proof of identity.
Agent checks updates and machine security.
Encrypted connection only to the approved resource.
Each connection is recorded for auditing.
ERP access for 14 days, limited to an authorized machine.
Posture checked on every connection.
Access expires on schedule or when the machine becomes unsafe.
A CVE — a publicly identified security flaw — is published.
dome checks the alert against inventory in minutes.
Affected machines listed; patch proposed.
You approve remediation.
Unpatched machines lose access to sensitive systems until fixed.
Investigation example: unsigned process + C2 connection + credential access.
Verdict: MALICIOUS · 95% confidence · awaiting approval
SOLUTIONS BY CHALLENGE
Illustrative use scenarios; results depend on the environment.
BEFORE
A malicious file goes unnoticed; hours later, the ransom demand appears.
AFTER
AI flags the process and connection; the team approves stopping it before encryption. After hours, autopilot can act without waiting for anyone.
BEFORE
Weeks collecting tickets and spreadsheets.
AFTER
Reports gather gaps and evidence to support auditing.
BEFORE
Hours correlating logs after a strange password request.
AFTER
AI finds the program, browser-data access and connection; you approve isolation.
BEFORE
Broad network access and slow-VPN tickets.
AFTER
Identity and posture verified. Only the authorized database is accessible.
dome by 33TS / Pricing
From 25 endpoints. Choose your level of protection.
Annual contract. Prices per endpoint/month.
from
US$3.00
per endpoint/month
from
US$7.00
per endpoint/month
from
US$10.00
per endpoint/month
Custom quote
dome MDR operated by 33TS (24×7) · Extended retention · 33TS incident response retainer
Minimum 25 endpoints. Servers count as 2 endpoints in Protect and Complete. Prices exclude taxes.
MONTHLY ESTIMATE
dome Complete · 100 billable endpoints
US$1,000.00
Estimate for separately contracting EDR, vulnerability management, patching and zero-trust access for the same number of machines.
US$2,300.00
USD base values supplied for this simulation: EDR US$ 15 + vulnerabilities US$3 + patch US$ 3 + ZTNA US$10 per remote user. EDR, vulnerabilities and patching are per machine/month. This is not a vendor quote or a verified market average; feature equivalence depends on the purchased products.
In dome Complete, ZTNA is already included per endpoint — without adding a remote-user charge.
No surprises after signing. Anything not in the per-endpoint price is listed here.
Each computer running the agent. Servers count twice in Protect and Complete, once in Essentials. Minimum 25.
Essentials offers a 30-day trial. Request activation; 33TS will confirm activation terms.
Ask 33TS or a partner for a volume quote. Above 2,000 endpoints, request Enterprise.
Yes. Request a partner contact or explore the channel program.
No. 24×7 dome MDR operated by 33TS is a separately contracted add-on.
ZTNA is included in Complete per endpoint. US$10 per remote user is only an assumption for the separate-solutions simulation.
dome by 33TS / Partners
Multi-tenant, monthly usage billing and white-label reports.
Operate multiple customer environments with a shared view.
Deal registration and protected margins.
Bring detection, remediation and access into one proposal.
Insurers, brokers, auditors and law firms.
Connect customers with a 33TS security operation.
Increasing benefits at each level
AuthorizedGoldPlatinumINDUSTRIES
A retail chain’s needs differ from those of a financial institution or a manufacturer. In the 30-minute conversation, we assess your specific scenario.
Distributed environments, hundreds of devices and remote branches: visibility and fast response for lean teams.
Endpoint protection, traceability, access control and evidence for compliance.
Availability, data protection and service continuity — without stopping the operation.
Many third parties accessing the environment: temporary, verified access with automatic expiration.
MANAGEMENT AND OPERATIONS
People who manage risk need to justify spend and show results. dome provides the numbers and reports for that — and scales for those serving many companies.
Risks, vulnerabilities, incidents and compliance in a view ready for leadership.
Compliance indicators against the main frameworks, for audits and risk management.
Each customer kept separate, central management and a white-label option.
Response times set in the contract, not generic promises.
dome · a 33TS product
In a 30-minute conversation, see the platform and assess which capabilities fit your team.